
Research, experiments, and implementation notes filed under security.
The eMudhra CA Compromise Is a Runtime Patch Problem
Eight eMudhra intermediate CA keys were recoverable from public certificates. Browsers moved quickly, but runtimes, containers, proxies, and embedded clients need explicit trust-store updates and tests.
Chrome DevTools MCP 1.12 Can Reload Agent Browser Policy Live
Chrome DevTools MCP 1.12 can reload URL restrictions and tool settings without a restart, while adding offline heap analysis and parallel page-scoped work.
Cloudflare's Brotli WAF Rules Start in Log Mode for a Reason
Cloudflare added emergency WAF detections for Brotli request bodies and the Next.js image endpoint, but operators should audit inherited overrides before changing either rule from Log to Block....
GitHub's Package Firewall Adds an Install-Time Gate for npm
GitHub's package firewall can hold back new npm releases, block known malware and vulnerabilities, and flag supply-chain regressions before agents or CI install them.
GitHub AI Scan Expands Pull Request Security Coverage, but It Won't Block Merges
GitHub AI Scan now checks pull request changes in PHP, Bash, Terraform, Dockerfiles, and other gaps in CodeQL coverage, with advisory findings and separate AI-credit billing.
Protected Quick Tunnels Make Agent Previews Less Risky
Cloudflare added free email protection to accountless Quick Tunnels, giving local agent previews a lightweight access gate without creating a Cloudflare app.
Dynamic Workers Make Agent Sandboxes Cheaper To Throw Away
Cloudflare Dynamic Workers move agent code execution into short-lived isolates, which is a practical shape for sandboxing generated JavaScript with narrow capabilities.
Copilot Local Sandboxing Makes Agent Permissions Concrete
GitHub Copilot app local sandboxing turns agent permissions into per-project policy, which is the right default shape for developer machines.
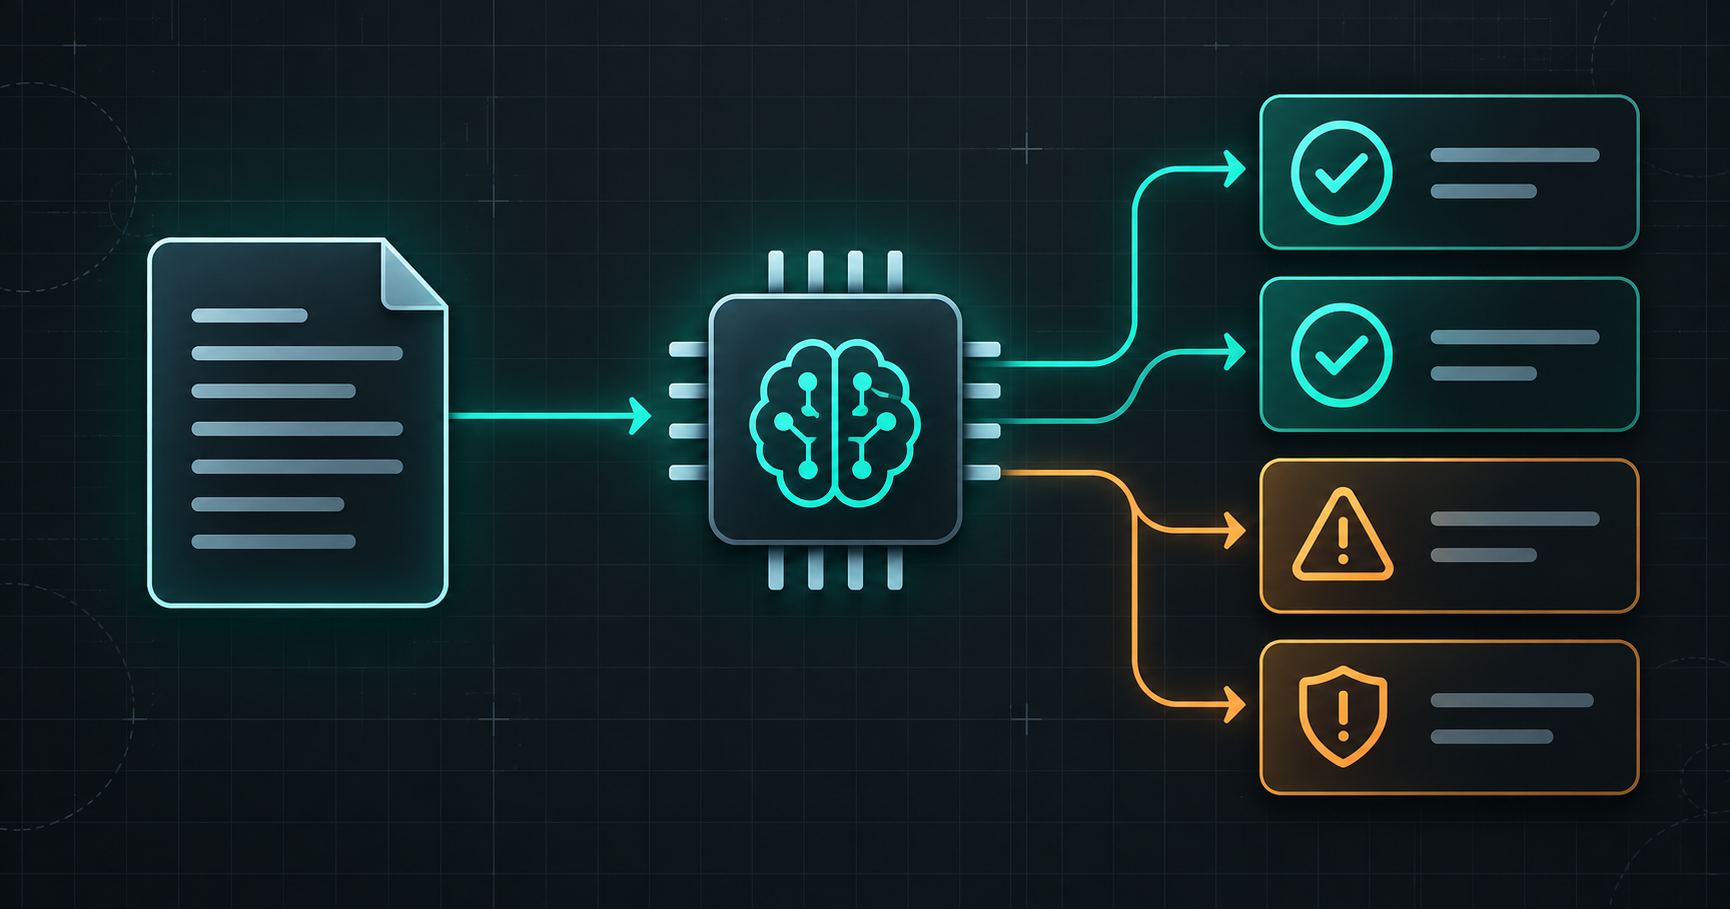
gpt-oss-safeguard Makes Safety Policies Runtime Inputs
OpenAI's gpt-oss-safeguard release turns written safety policies into runtime classifier inputs, which is useful for teams that need adaptable Trust and Safety workflows.
GitHub Coverage Rulesets Are Now Scriptable
GitHub added REST API support for code coverage ruleset thresholds, making coverage gates easier to manage across repositories without clicking through settings screens.
Cloudflare Workers Access Can Now Be Scoped Per App
Cloudflare added resource-level roles for Workers, giving teams a cleaner way to give CI systems, teammates, and coding agents only the access one application needs.
GitHub Advanced Security Configurations Can Now Be Enforced
GitHub enterprise administrators can now enforce Advanced Security configurations against both repository and organization owners, closing a practical policy gap for large teams.
GitHub Copilot Code Review Gets Closer to Real CI
GitHub Copilot code review now uses broader shell tools and an ensemble of agents in Lite reviews, which makes AI review more useful but also worth treating like...
Cloudflare 1.1.1.1 Makes Post-Quantum DNSSEC Practical to Test
Cloudflare's 1.1.1.1 resolver now validates ML-DSA-44 DNSSEC signatures, exposing the real migration work: large packets, TCP fallback, downgrade policy, and parent-chain adoption.

GitHub Actions Cache Mode Makes CI Caches Less Trusting
GitHub Actions cache-mode is now generally available, giving workflows and jobs explicit read, write, write-only, or no-cache access so teams can reduce cache-poisoning risk.
Cloudflare Automatic Key Exchange Makes Post-Quantum Origin TLS Less Manual
Cloudflare's Automatic Key Exchange measures each origin's TLS 1.3 key agreement support, then leads with the strongest safe key share, including X25519MLKEM768 where origins support it.
Cloudflare Connects AI Vulnerability Hunting To Production Evidence
Cloudflare's Vulnerability Discovery and Remediation service is a useful pattern for AI security work: rank findings with production traffic, WAF context, validation, and human review.
OpenAI Agents SDK Makes Sandboxes A First-Class Boundary
OpenAI's Agents SDK update is a practical reminder that production agents need explicit workspaces, isolated compute, durable state, and credential boundaries.
Codex Turns Agent Runtime Into Platform Work
OpenAI's Codex platform post is a practical reminder that useful agents need runtime boundaries, product-owned context, streaming, and approval flows, not just a chat box.
Cloudflare BotBase Makes Bot Identity Operational
Cloudflare's BotBase for Operators is a practical reminder that agent and crawler teams need identity, behavior declarations, and verification before traffic gets blocked.
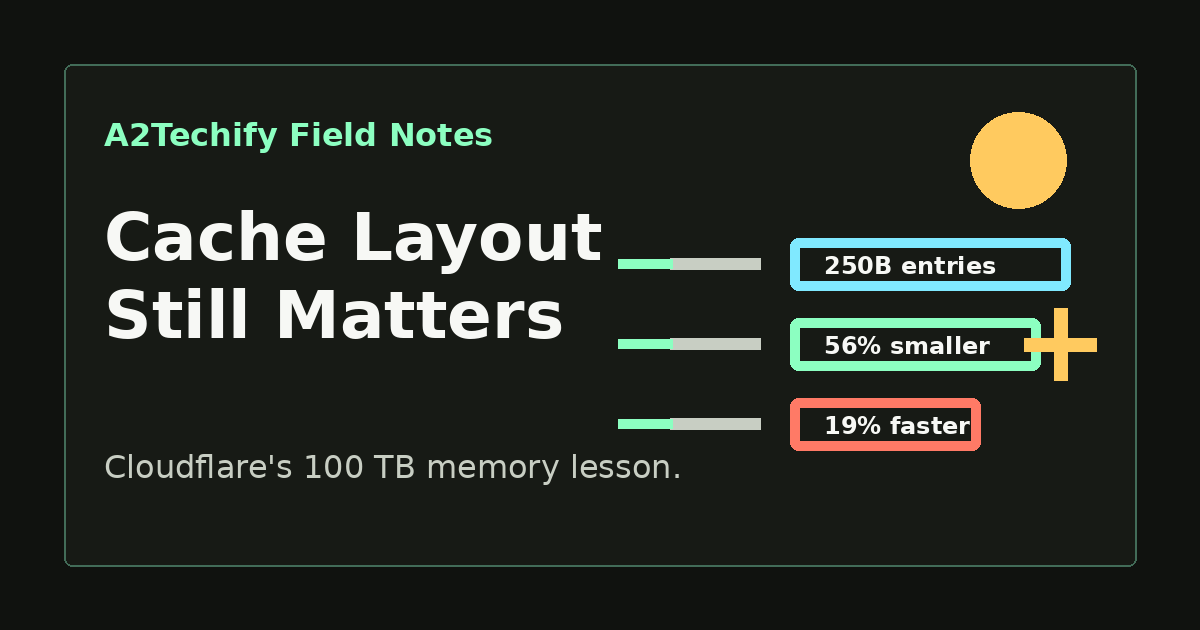
Cloudflare Shows Why Cache Layout Still Matters
Cloudflare's 1.1.1.1 DNS cache work is a practical reminder that high-cardinality systems need memory layout reviews, not just bigger machines.
GitHub Rule Insights Make Repository Governance Easier To See
GitHub's rule insights dashboard is now generally available at repository and organization levels, giving teams a faster way to audit ruleset failures, bypasses, and enforcement trends.
Cloudflare Bot Preference Sync Keeps AI Crawler Policy Honest
Cloudflare's Bot Preference Sync turns AI bot policy into a generated robots.txt block, reducing drift between what a site says to crawlers and what it enforces at the...
Docker Sandboxes Put CI Agents Behind a Smaller Boundary
Docker's GitHub Agentic Workflows integration gives coding agents a microVM sandbox with a private Docker daemon, making CI automation more useful without handing it the whole runner.
Cloudflare OAuth Makes Agent Permissions Less All-Or-Nothing
Cloudflare's optional OAuth scopes give agent and MCP builders a practical way to request broad capability while letting users approve a narrower task-based grant.
Cloudflare Workers Shows Why Isolation Needs Layers
Cloudflare's Workers Spectre reassessment is a practical reminder that isolate-based platforms need layered containment, not a single clever mitigation.
Coding Agent Allowlists Are Not A Security Boundary
A practical look at why trusted-command allowlists can fail for coding agents, and what teams should move into the sandbox boundary instead.
GitHub's License Data Update Makes SBOM Reviews Less Noisy
GitHub is prioritizing registry license metadata in the dependency graph, which should make SBOMs and dependency review checks easier to trust.
What MCP Traffic Detection Can—and Cannot—Protect
Where Cloudflare's MCP traffic detection helps, where it cannot, and which controls still belong at the server.